Triage the complete signal
Establish the symptoms, business impact, affected environment, available evidence, responsible owners, and actions already taken before changing production.
If your WordPress website is redirecting visitors, displaying spam, creating unfamiliar users, triggering browser warnings, or behaving in ways your team cannot explain, the visible symptom may be only one part of the incident.
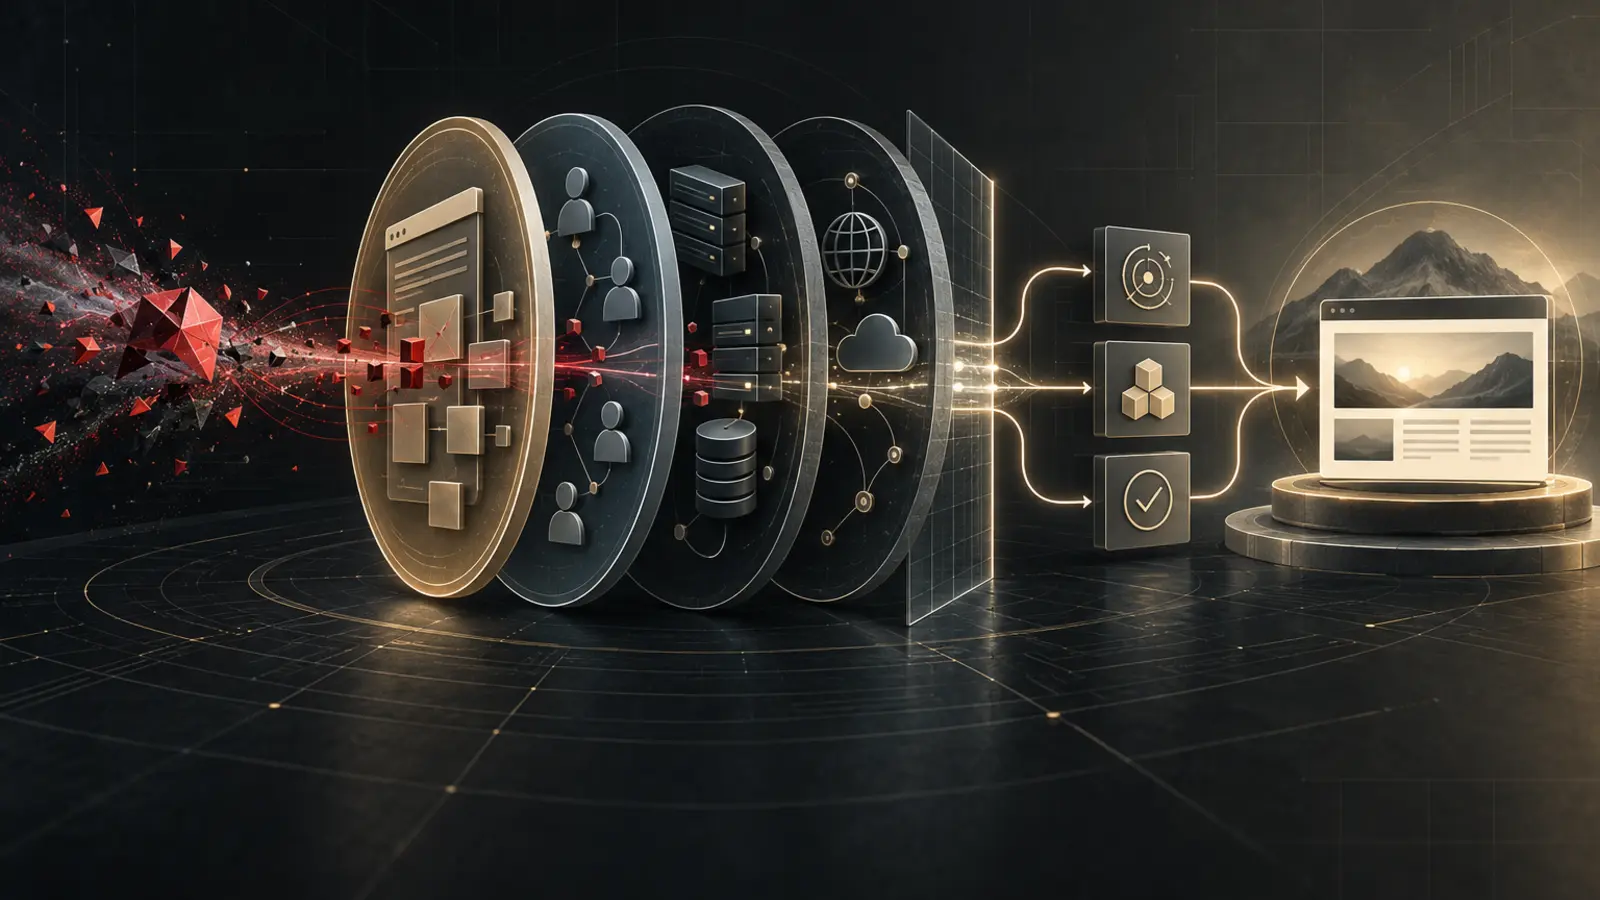
Establish the symptoms, business impact, affected environment, available evidence, responsible owners, and actions already taken before changing production.
Preserve relevant evidence, quarantine confirmed harm, follow persistence beyond the visible file, and recover WordPress or the underlying host from defensible sources.
Test the effective controls and critical journeys, document what was established, and create a maintained baseline for monitoring, patching, backup, and recovery.
Responsible WordPress malware removal determines what changed, whether malicious access or persistence remains, which parts of the environment can still be trusted, and what evidence supports returning the site to service. Deleting a flagged file may remove a symptom while leaving behind a stolen credential, database injection, scheduled task, unsafe execution path, or compromised server.
Osiris examines the WordPress application and the infrastructure around it in proportion to the evidence. Scanners, checksums, file monitoring, logs, and AI-assisted analysis can accelerate discovery, but none replaces technical judgment. Production changes are scoped, reversible where practical, and paired with validation.
Redirects, injected search results, browser warnings, unexpected administrators, modified core files, PHP inside uploads, recurring reinfection, unfamiliar processes, and unexplained outbound activity all warrant triage. They do not all prove the same thing. An unfamiliar file might be malicious, legitimate customization, a generated artifact, or an old ownership-verification file.
Classification comes before destructive action. The objective is to understand what the signal means, what trust boundary it affects, and whether the immediate priority is visitor safety, evidence preservation, availability, credential containment, or clean reconstruction.
Core, plugins, themes, custom code, uploads, users, database content, scheduled events, configuration, and rewrite behavior are only the application layer. PHP, the web server, file ownership, operating-system packages, DNS, TLS, caching, CDN rules, management panels, and connected services can determine whether a control actually works.
Official checksums help establish core integrity, but they do not explain an unauthorized extra file placed beside trusted code. Premium software and custom components may lack public checksums. Osiris therefore evaluates provenance, privilege, behavior, ownership, and business purpose rather than treating every checksum exception as malware—or every checksum success as proof of safety.
Record symptoms, access, hashes, metadata, configuration, accounts, logs, and observed behavior. Create a recoverable protected copy when circumstances permit.
Restrict the unsafe path, process, account, or public behavior without confusing containment with complete recovery.
Replace official components from matching trusted releases, review custom assets deliberately, and exclude unauthorized additions.
Test integrity, access, persistence, effective controls, HTTPS, forms, administration, integrations, and representative visitor journeys.
The first response establishes authority, scope, current impact, important business functions, and the people who own access. Availability matters, but it cannot automatically take precedence over visitor safety or evidence. Depending on the incident, containment may disable a malicious account, isolate executable uploads, restrict a compromised component, stop a process, or place the site into a controlled maintenance state.
The investigation then follows the trust boundary. A suspicious WordPress file may remain an application-level event, or it may lead to operating-system services, interactive access, credentials, and network activity. If privileged compromise is established, hardening the same live host can reduce immediate exposure but cannot restore a trustworthy root. A clean-host reconstruction becomes the responsible recovery path.
Official WordPress files can be reconstructed from the matching trusted release. Supported plugins and themes can be replaced from known packages. Custom code, commercial components, media, configuration, and business data require deliberate review because they may be irreplaceable while still carrying uncertainty. Backup completeness and clean provenance are related, but they are not the same claim.
Access is reconciled at the same time. WordPress administrators, application passwords, hosting accounts, SSH and SFTP users, deployment keys, database access, DNS administration, and connected services each need a current owner and purpose. Credential rotation is coordinated with those owners, and temporary access is removed after the approved work.
Validation must match the statements being made. A clean scanner result is useful supporting evidence, but it cannot prove that a stolen credential was revoked, a scheduled persistence mechanism was removed, PHP cannot execute in a writable upload path, or a reconstructed website still completes its important forms and integrations. Osiris tests the controls and journeys that matter to the incident and records the result.
The final record separates confirmed findings, actions completed, successful checks, unresolved limitations, and recommended follow-up. This becomes the baseline for proactive maintenance: managed updates, monitored backups, access governance, vulnerability and integrity review, certificate observation, escalation, and periodic recovery testing.
To request triage, provide the public URL, what changed, when it was first observed, whether visitors or business workflows are affected, what the host or security provider reported, and who is authorized to approve access and remediation. Do not send passwords, private keys, customer data, or sensitive indicators through the public form.
Related guidance explains what to do when a WordPress website is compromised and why a clean malware scan is not enough. Our anonymized server compromise recovery case study shows how a suspicious application signal can require a wider infrastructure response.
Sometimes, but availability cannot take precedence over visitor safety or evidence. The response may keep unaffected functions online, restrict only the compromised path, use a staged replacement, or require a temporary maintenance state. The decision depends on the observed behavior and consequence of continued exposure.
No single scan proves whole-system recovery. Scanners can miss extra files, stolen credentials, database changes, scheduled persistence, unsafe server configuration, compromised connected accounts, or indicators outside their rules. A clean result is useful when combined with integrity checks, access review, effective-control testing, and functional validation.
Reinfection can result from a missed entry point, a persistence mechanism, a stolen credential, a vulnerable or abandoned component, another compromised account, an unsafe hosting neighbor, or restoration from an infected backup. Deleting the visible symptom without resolving the underlying access or persistence path allows repetition.
A complete investigation commonly requires WordPress administrator access plus a file or server-level path such as SFTP, a hosting panel, or SSH. The exact access is established after initial triage. Temporary individual accounts and least privilege are preferred, and credentials should never be submitted through the public form.
A missing clean backup increases risk but does not always make recovery impossible. Preserve the current state before destructive work. Core and supported dependencies may be reconstructed from trusted sources, while custom code, media, configuration, and database content require careful review and tested transfer.
A clean-host rebuild is appropriate when privileged attacker access is confirmed or when the integrity of the operating system and control plane cannot be established. Cleaning selected files on an untrusted host may reduce visible symptoms without restoring a dependable root of trust.
Osiris investigates likely entry and persistence paths using the evidence available. Historical certainty may be impossible when logs are incomplete, accounts were shared, or the environment was already overwritten. Findings distinguish confirmed facts, supported hypotheses, and unanswered questions.
Recovery should lead to a maintained baseline: managed updates, monitored backups, access governance, vulnerability and integrity review, uptime and certificate observation, documented escalation, and periodic recovery testing. Ongoing stewardship reduces both the likelihood and consequence of another incident.
Bring us the platform that needs stronger engineering, tighter security, or a clear technical owner.